CAREERS ENCYCLOPEDIA
SIEM Engineer
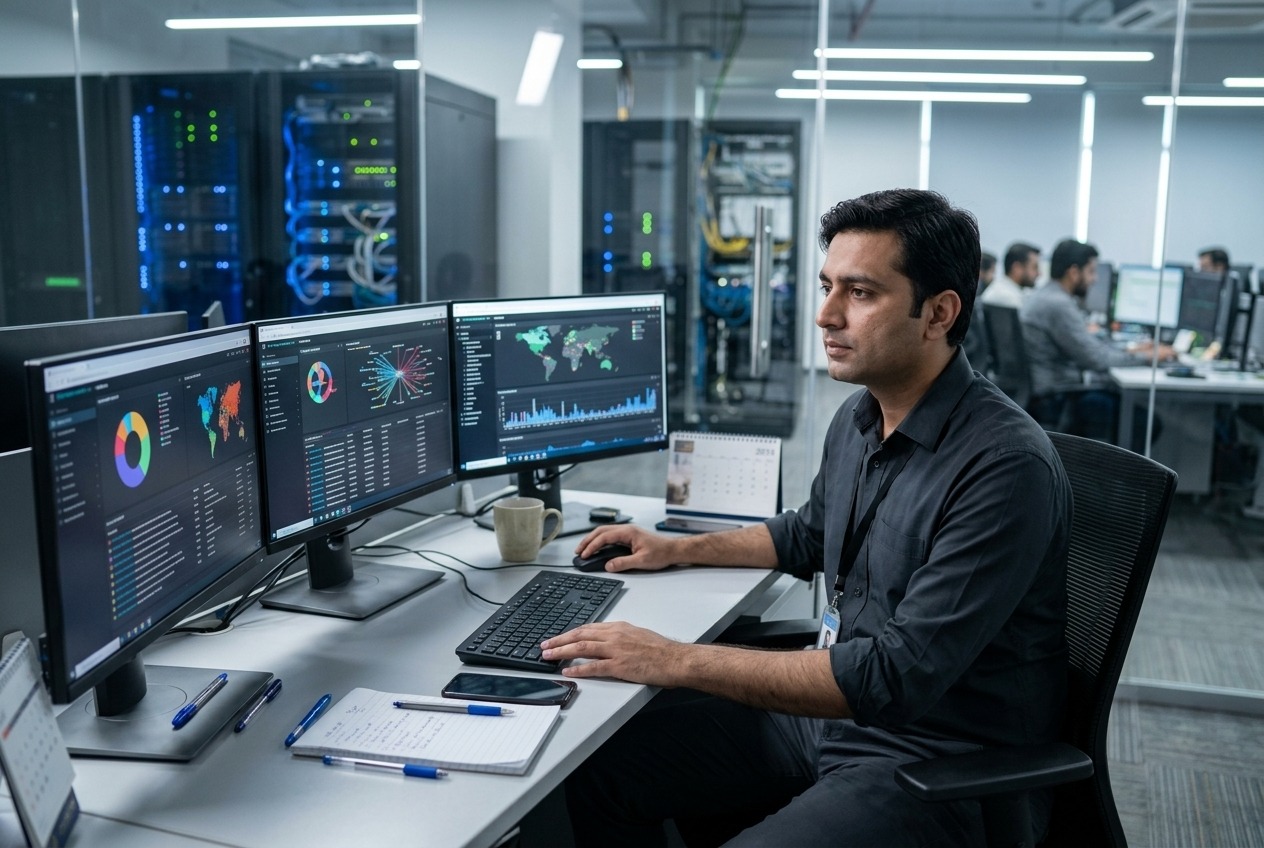
A SIEM Engineer designs, implements, and maintains Security Information and Event Management systems to monitor computer networks, detect cyber threats, and investigate security incidents. They collect and analyze security logs, configure alerts, and help organizations protect their systems and sensitive information.
- Configure and maintain SIEM platforms.
- Collect and monitor logs from servers, networks, and applications.
- Create rules to detect suspicious activities.
- Investigate security alerts and potential threats.
- Develop dashboards and security reports.
- Integrate security tools with SIEM systems.
- Reduce false alerts and improve detection accuracy.
- Support incident response and security investigations.
- Maintain monitoring procedures and technical documentation.
- Collaborate with security analysts and IT teams.
Cybersecurity Fundamentals
- Understand common cyber threats and attacks.
- Know security controls and incident response procedures.
- Understand authentication and access management.
Networking and Operating Systems
- Understand network protocols and traffic patterns.
- Know Windows and Linux system logs.
- Understand servers, firewalls, and endpoint security.
SIEM Systems and Log Management
- Understand log collection and event correlation.
- Know alert rules and security monitoring methods.
- Understand threat detection and investigation processes.
SIEM Configuration
- Configure log sources and data collection.
- Develop detection rules and dashboards.
- Maintain SIEM integrations and monitoring settings.
Threat Analysis
- Investigate suspicious events and security alerts.
- Identify unusual patterns in system logs.
- Support the detection of malware and unauthorized access.
Technical Troubleshooting
- Resolve log collection and parsing issues.
- Improve alert accuracy and system performance.
- Document technical problems and their solutions.
Analytical Ability
- Interpret large volumes of security events.
- Identify relationships between suspicious activities.
- Recognize unusual system behavior.
Problem-Solving Ability
- Investigate technical security problems.
- Determine possible causes of alerts.
- Recommend improvements to detection systems.
Attention to Detail
- Review logs for small but important indicators.
- Check detection rules for errors.
- Maintain accurate investigation records
Work with Splunk Enterprise Security.
- Use Microsoft Sentinel for security monitoring.
- Work with IBM QRadar or Elastic Security where applicable.
Security Monitoring Tools
- Use firewalls and endpoint detection tools.
- Review network traffic and system logs.
- Integrate threat intelligence sources.
Scripting and Data Tools
- Use Python or PowerShell for automation.
- Write queries to search and investigate events.
- Use Linux command-line tools for troubleshooting.
A SIEM Engineer is analytical, careful, curious, patient, and responsible.
They do well at jobs that need:
Logical Thinking: Examines security events systematically.
Attention to Detail: Notices unusual activities.
Curiosity: Investigates unfamiliar threats.
Patience: Reviews complex technical evidence.
Responsibility: Handles security information carefully.
Continuous Learning: Keeps up with changing cyber threats.
- A bachelor's degree in Computer Science, Information Technology, Cybersecurity, or a related field.
- Knowledge of computer networks and operating systems.
- Understanding of security logs and incident response.
- Practical experience with at least one SIEM platform.
- Basic scripting knowledge in Python or PowerShell.
- Familiarity with security frameworks and threat detection methods.
- Hands-on practice through labs, internships, or security projects.
- Relevant certifications can improve employment opportunities.
SIEM Engineers are employed by organizations that need continuous security monitoring and cyber threat detection. Opportunities exist in IT companies, banks, telecom operators, government departments, managed security service providers, and large businesses. With experience, professionals may progress to Senior SIEM Engineer, Security Operations Center (SOC) Engineer, Security Architect, or Cybersecurity Manager.
- Cybersecurity companies.
- Banks and financial institutions.
- Telecom companies.
- Software houses and IT service providers.
- Government and public-sector organizations.
- Managed security service providers.
- Healthcare organizations.
- E-commerce and online service companies.
- Large manufacturing and energy companies.
- Security Operations Centers.
- BS Computer Science.
- BS Information Technology.
- BS Cybersecurity, where available.
- BS Software Engineering.
- BS Computer Engineering.
- Master's degree in Cybersecurity or Information Security.
- Short courses in SIEM, networking, and security operations.
- Practical training in log analysis and incident response.
- National University of Sciences and Technology (NUST), Islamabad.
- Air University, Islamabad.
- COMSATS University Islamabad.
- FAST National University of Computer and Emerging Sciences.
- Bahria University, Islamabad.
- Information Technology University, Lahore.
- Virtual University of Pakistan.
- Pakistan-based cybersecurity training providers offering relevant technical courses.
- Public university bachelor's degree: PKR 60,000 to 250,000 per year.
- Private university bachelor's degree: PKR 150,000 to 700,000 per year.
- Master's degree in a relevant field: PKR 200,000 to 1,000,000 or more in total.
- Networking and cybersecurity courses: PKR 10,000 to 60,000.
- SIEM platform training: PKR 20,000 to 100,000.
- Professional certification preparation: PKR 15,000 to 80,000, excluding examination fees where applicable.
- Practical labs and study materials: PKR 10,000 to 40,000.
- Scholarships and financial assistance: Eligible students may receive 25% to 100% tuition support through university merit scholarships, need-based aid, and applicable government programs.